Skip to content

Securing Medical AI: Adversarial Attack Detection and Mitigation in CAD Systems

Oct 2026 · IEEE Transactions on Emerging Topics in Computational Intelligence · Vol 10, pp. 3836-3848 · 0 citations · 49 references

Abstract

Frequency-constrained adversarial attacks introduce imperceptible, high-frequency distortions that undermine the reliability and safety of AI-assisted medical diagnostics, posing a serious challenge to trust and resilience in socially-interactive, human-AI healthcare systems. To address this, we introduce Sentinel, a pioneering framework that detects, classifies, and mitigates adversarial attacks in medical image analysis without requiring training or model specificity. Sentinel integrates a lightweight detection module that uses a confidence scorer to analyze predictions from multiple low-rank approximations of the input image, enabling precise classification of attacks as either gradient-based or frequency-constrained. Uniquely, Sentinel includes a recovery module specifically designed for frequency-constrained attacks, employing adaptive Robust Principal Component Analysis-based denoising to suppress perturbations concentrated in smaller singular values while preserving essential image structure. This allows for effective image reconstruction, an area overlooked by existing methods. Evaluated across four diverse medical imaging datasets, Sentinel demonstrates consistently high detection accuracy, classification performance, and adversarial recovery without the need for model retraining or GPU support, making it a highly practical and scalable solution for integration into clinical AI systems. Additional explainability analyses confirm the reliability and interpretability of Sentinel's predictions, establishing it as a significant advancement in adversarial defense.

View source

Similar papers

Sep 2026

Seeing Through Threats: Adversarial Detection Through Explainability (ADEx)

Deep Neural Networks (DNNs) remain vulnerable to adversarial perturbations, raising significant concerns in image processing applications, particularly in high-stakes domains such as medical imaging and security-critical systems. Most existing defense strategies are limited by domain specificity, architectural dependen...

Syamantak Sarkar, Nirmal Joseph, Sudhish N. George et al. · 0 citations
Conference Aug 2026

Advances in Detecting and Mitigation Adversarial Manipulations in Medical Imaging: A Review

Medical Image Analysis has seen remarkable improvements with Deep Learning (DL), which have helped in refining the accuracy of disease detection, diagnosis, and clinical decision support. But these models are still very vulnerable to Adversarial Attacks, in which subtle yet carefully engineered perturbations can lead t...

Drashti Deveshbhai Patel, Jaimeel Shah, A. Kushwaha · 0 citations
Open access Sep 2026

PatchGuard-Freq: Zero-Overhead Adversarial Patch Defense via Frequency Detection and Data-Driven Robustness

This work characterizes the complementary relationship between reconstruction-based and robustness-based paradigms in the accuracy–efficiency design space under the evaluated conditions: the former suits compute-unconstrained scenarios while the latter serves latency-constrained deployments.

De-Jie Luan, Cheng-Hua Li, Chun-Jie Zhang et al. · 0 citations

Transportability of Adversarial Attack Transportability of Adversarial Attack

This study seeks to discern whether images featuring avatars can be effectively used to generate adversarial examples capable of fully masking a person, and establishes a method of utilizing virtual avatars to provide increased privacy for users.

Unknown authors · 0 citations
Open access Aug 2026

A Comprehensive AI Security Pipeline: Drift Detection, Adversarial Robustness and Automated ML Testing

The wide-scale uptake of machine learning applications in safety-sensitive applications renders modern AI deployments prone to adversarial attacks, statistical distribution changes, and various governance reliability issues. Current AI security methodologies generally handle the discussed issues separately, making the...

Siddharth Kumar, Siddhanth Harish Bist · 0 citations

Related blog posts

Microsoft Research Blog Nov 16, 2026

TokenEconomizer: Learning from Experience to Make AI Coding Agents More Efficient

AI coding agents are increasingly help developers fix bugs and build features largely on their own, but every interaction with their models consumes tokens. In each session, an agent sends instructions, tool descriptions, and session history to its model. Most efforts to reduce this cost focus on individual tasks. Yet developers return to the same […] The post TokenEconomizer: Learning from Experience to Make AI Coding Agents More Efficient appeared first on Microsoft Research.

GPT-Lab Nov 13, 2026

TenderIntell at ICSOB 2026: Three Days in Gothenburg

At ICSOB 2026 in Gothenburg, we presented TenderIntell, our work on multi-agent support for tendering. This post looks back at the conference, the idea behind a panel of three AI reviewers who score each proposal independently, and why evaluating agents reliably is the question we keep coming back to. The post TenderIntell at ICSOB 2026: Three Days in Gothenburg appeared first on GPT-Lab.

MIT News · Artificial Intelligence Nov 13, 2026

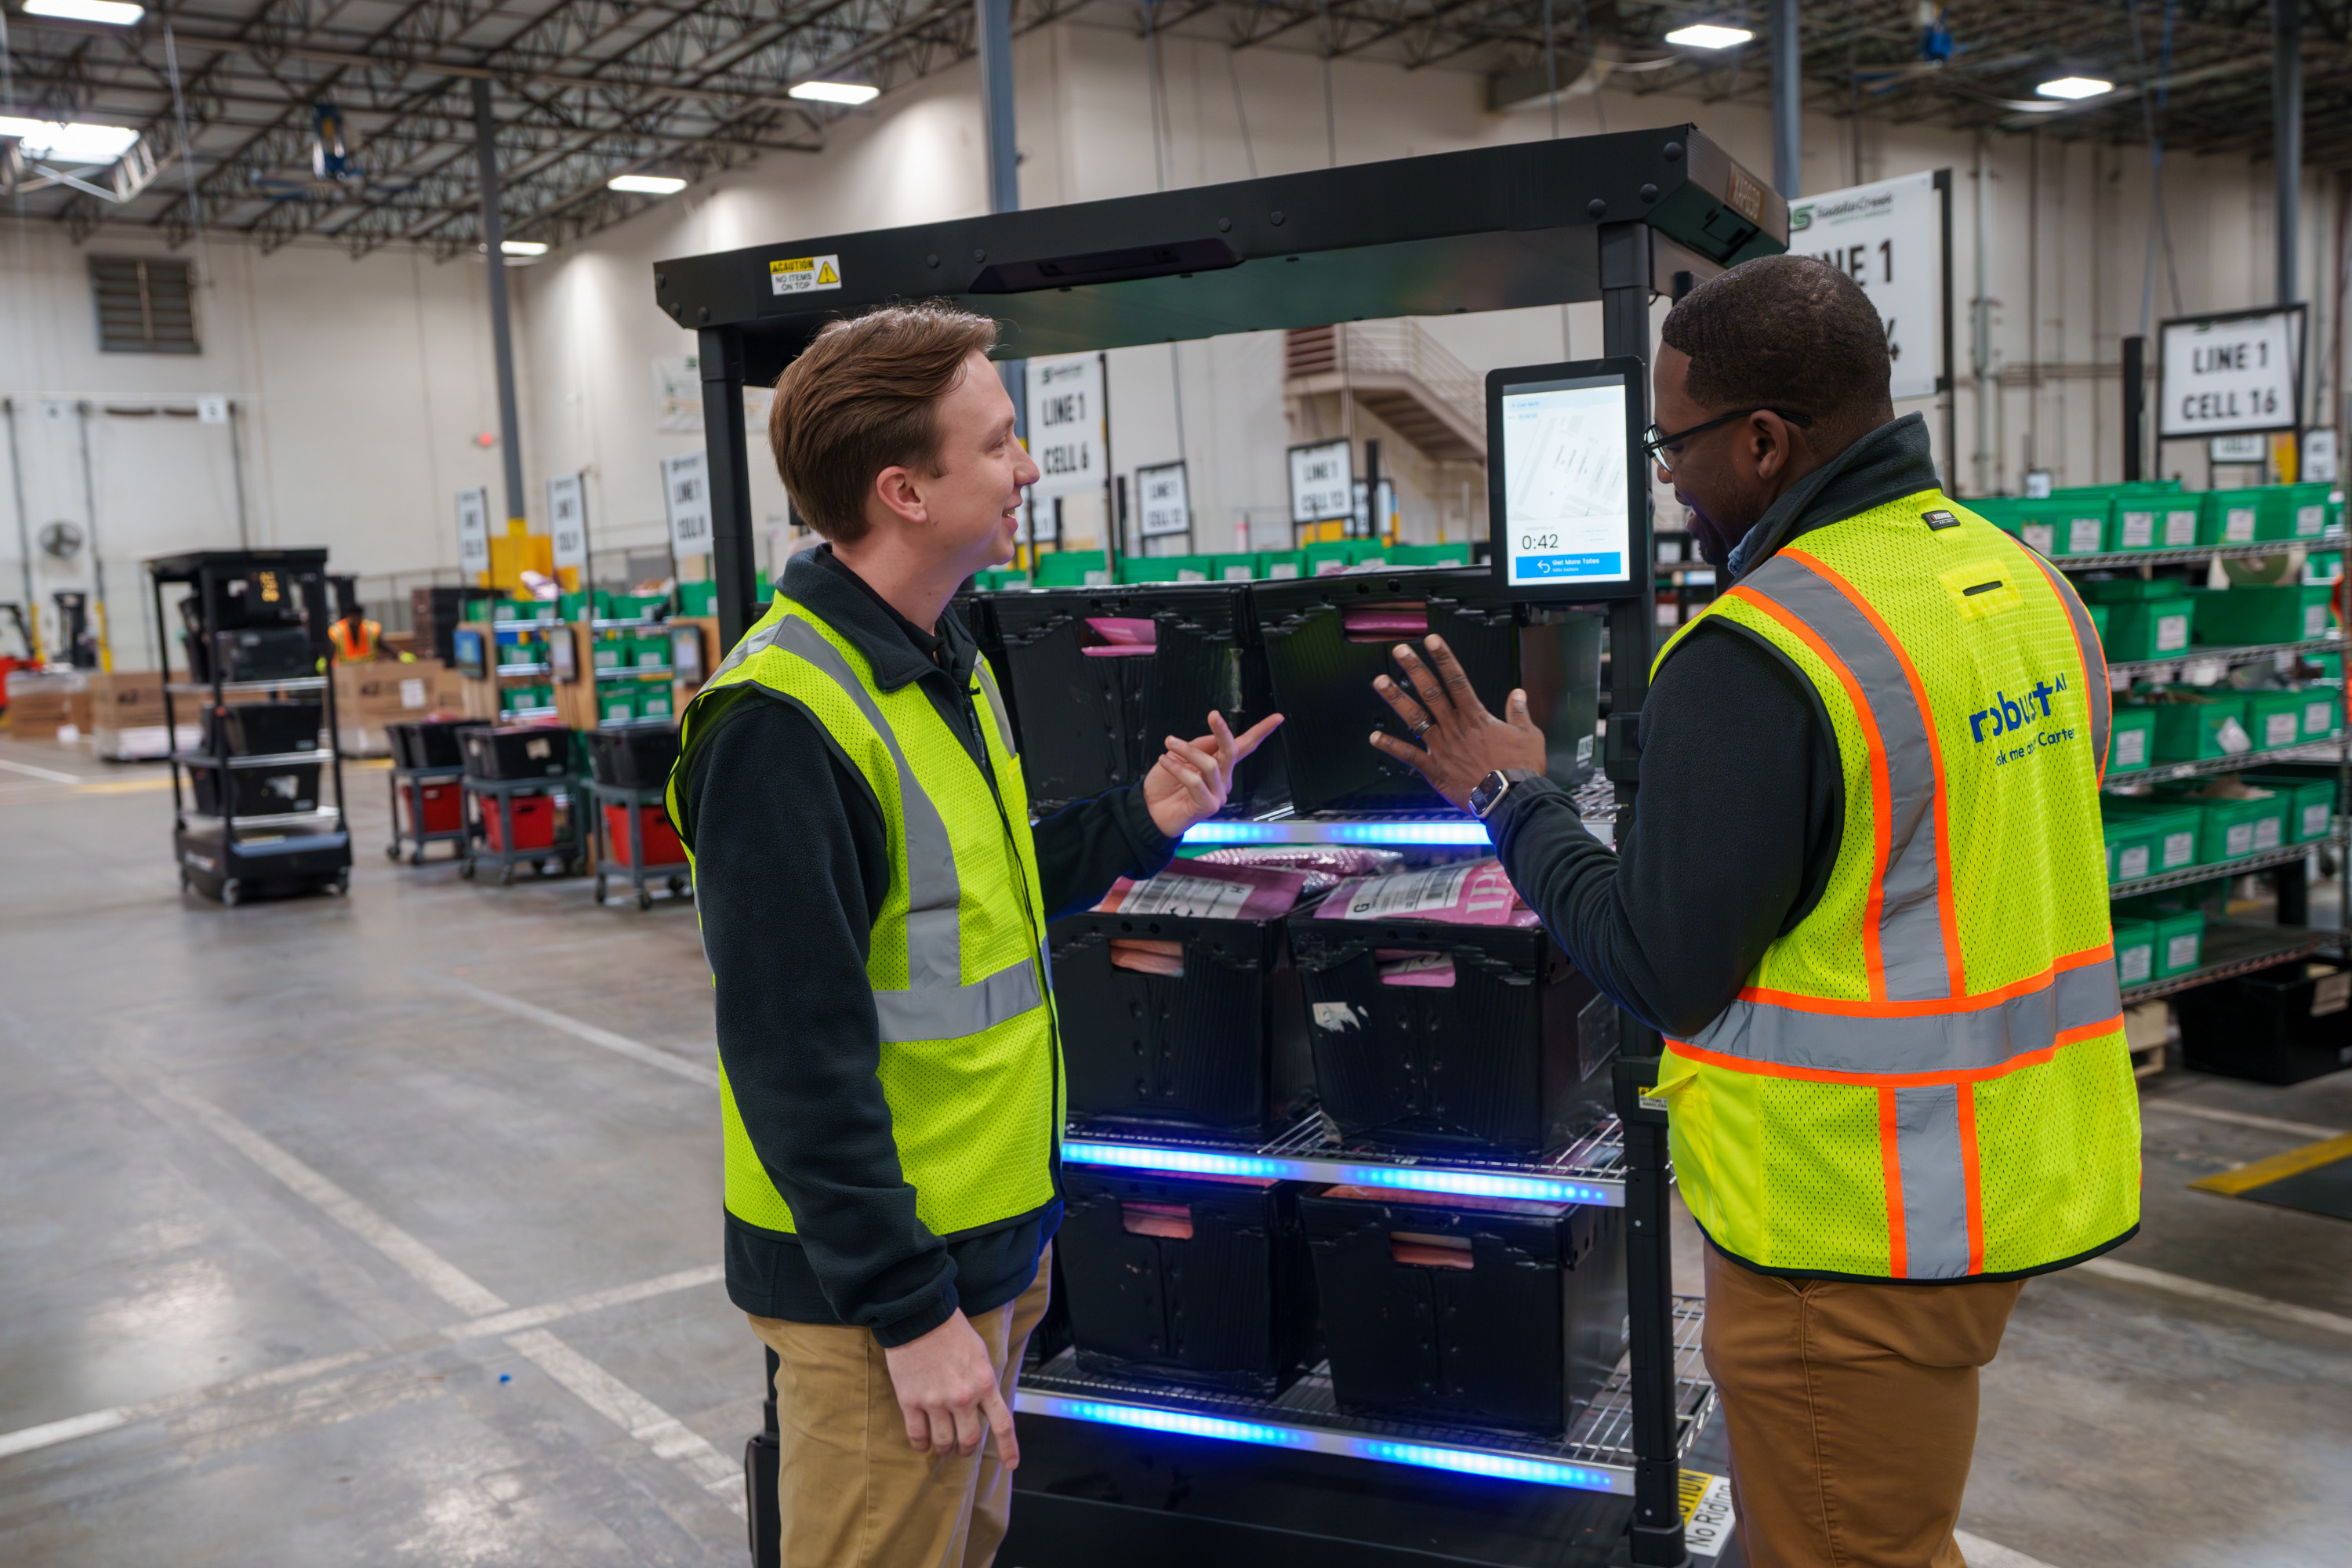
Helping robots fit into the human workplace

Founded by Anthony Jules ’92, SM ’92 and Professor Emeritus Rodney Brooks, Robust AI’s robots are designed to collaborate with humans in factories and warehouses.

We use cookies to run the site and, with your consent, for analytics and to show ads. See our Cookie Policy.