Oct 2026· IEEE Transactions on Emerging Topics in Computational Intelligence· Vol 10, pp. 3303-3323· 0 citations· 121 references
Abstract
Deep neural networks play a significant role in medical image analysis, particularly in improving the efficiency and accuracy of disease diagnosis and treatment planning. The ability to preserve the privacy of medical data opens the door to harnessing more information to train powerful and intelligent AI models. However, the added complexity introduced by incorporating privacy measures often leads to increasingly opaque deep learning models. As the need to interpret these privacy-preserving deep learning models grows, explainable AI systems have become pivotal for cultivating trust among clinical experts and stakeholders. To address this challenge, researchers have begun to focus on developing privacy-preserving techniques with improved explainability features. This article presents a comprehensive survey of different privacy models and security techniques, focusing on biomedical imaging applications. The survey covers peer-reviewed studies published during 2019–2024, ensuring comprehensive and contemporary coverage of privacy-preserving and explainability techniques. It covers a detailed review of various privacy-preserving methods and studies related to model explanations. It also highlights unresolved challenges and suggests potential research directions. This survey aims to offer valuable directions to the research community by explaining privacy-preserving techniques for medical image analysis.

This study offers a coherent analysis of present methods, unresolved issues, and future research paths, positioning their combined adoption as a fundamental necessity for next-generation medical and biometric imaging.
Ghazala Hcini, Imen Jdey· Multimedia tools and applica...· 0 citations
Summary Background Recent NIH Data Management and Sharing (DMS) policy updates and NIH controlled-access data security requirements have increased attention to facial anonymization and controlled-access handling of shared head imaging data. This is particularly relevant for datasets submitted to or hosted by the Cancer...
This work investigates privacy leakage in federated learning using the NIH Chest X-ray dataset by evaluating the susceptibility of three deep learning architectures namely Simple CNN, ResNet-50, and EfficientNet to gradient-based image reconstruction attacks and suggests that model architecture can deeply influence the...
Recent innovations in deep learning have significantly enhanced the diagnosis of medical images, although they are based on the use of centralized data storage that pose severe threats to patient privacy and medical data security. To address this issue, this research proposes a Federated Learning (FL) model that is cou...
Najiyya Younas, O. Abdulkader, Yaser Ali Shah et al.· 0 citations
Medical Image Analysis has seen remarkable improvements with Deep Learning (DL), which have helped in refining the accuracy of disease detection, diagnosis, and clinical decision support. But these models are still very vulnerable to Adversarial Attacks, in which subtle yet carefully engineered perturbations can lead t...
Drashti Deveshbhai Patel, Jaimeel Shah, A. Kushwaha· 2026 International Conferenc...· 0 citations
The analysis finds that noise-based methods such as DP remain the practical baseline but offer only partial protection; cryptographic approaches provide stronger theoretical guarantees at substantially higher cost; and LLM/multimodal leakage remains an urgent, under-benchmarked gap.
Subhasish Ghosh, A. K. Mandal· Knowledge and Information Sy...· 0 citations
Related blog posts
Microsoft Research Blog· microsoft.comNov 16, 2026
AI coding agents are increasingly help developers fix bugs and build features largely on their own, but every interaction with their models consumes tokens. In each session, an agent sends instructions, tool descriptions, and session history to its model. Most efforts to reduce this cost focus on individual tasks. Yet developers return to the same […] The post TokenEconomizer: Learning from Experience to Make AI Coding Agents More Efficient appeared first on Microsoft Research.
At ICSOB 2026 in Gothenburg, we presented TenderIntell, our work on multi-agent support for tendering. This post looks back at the conference, the idea behind a panel of three AI reviewers who score each proposal independently, and why evaluating agents reliably is the question we keep coming back to. The post TenderIntell at ICSOB 2026: Three Days in Gothenburg appeared first on GPT-Lab.
MIT News · Artificial Intelligence· news.mit.eduNov 13, 2026
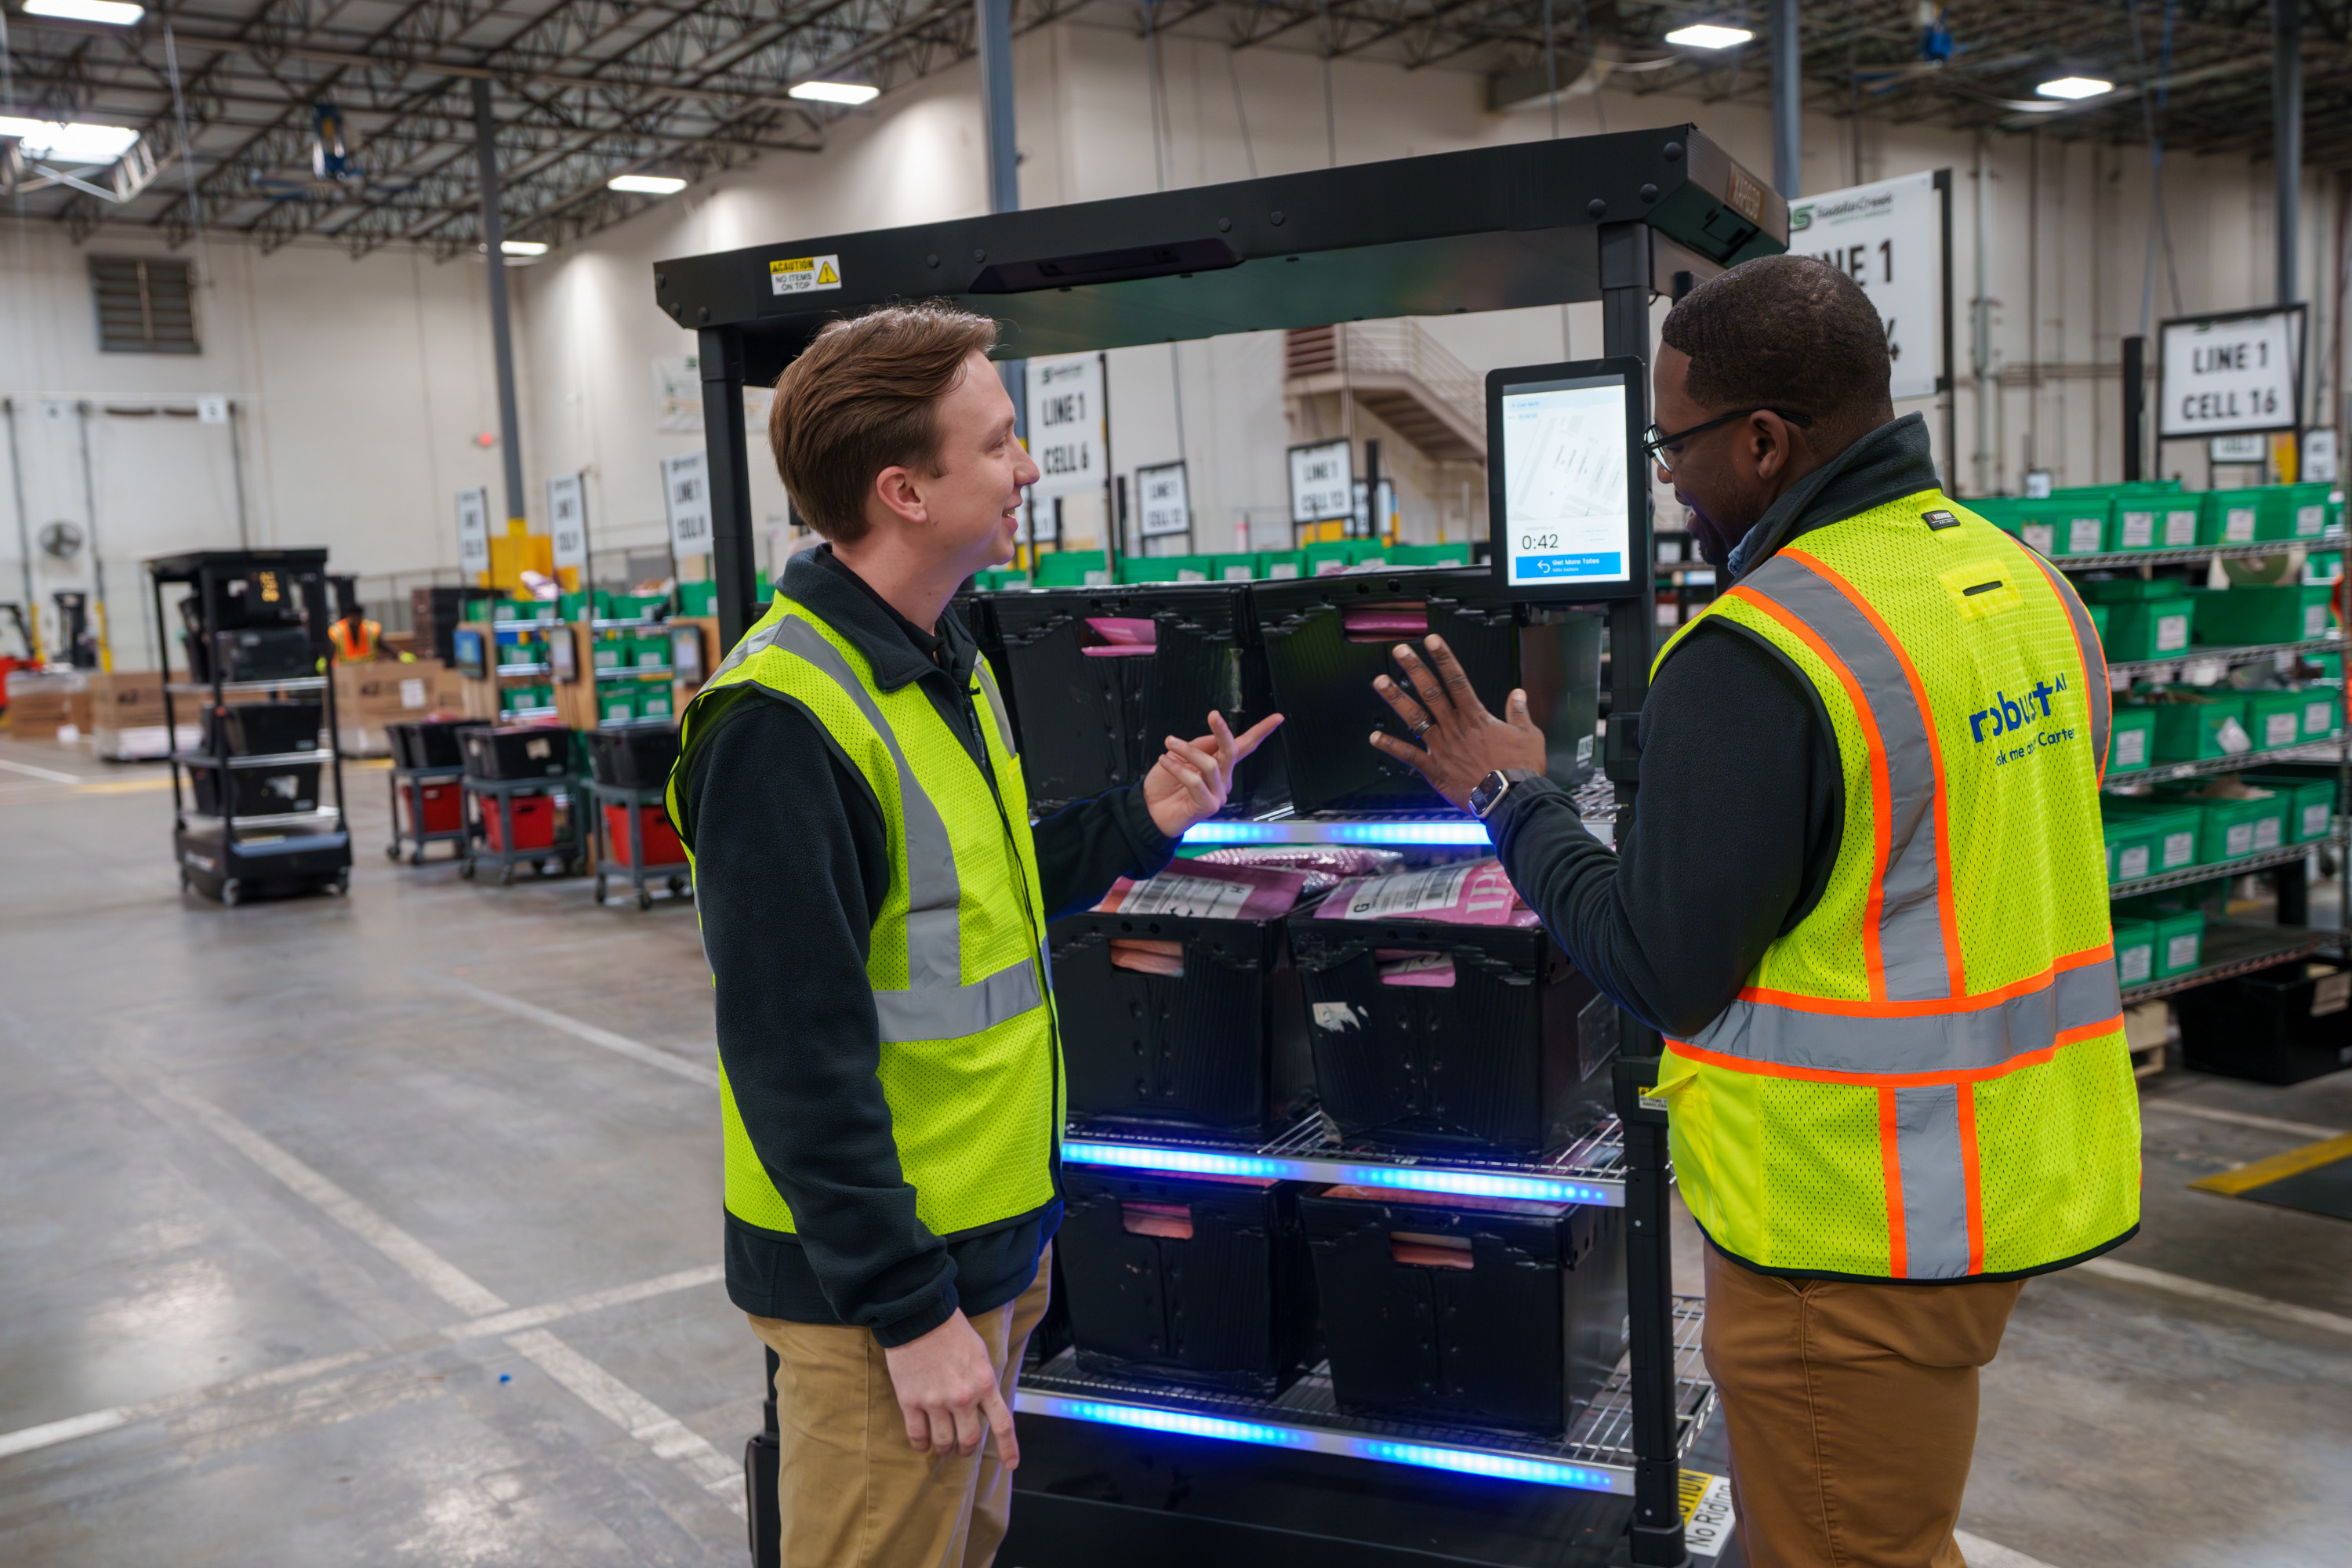
Founded by Anthony Jules ’92, SM ’92 and Professor Emeritus Rodney Brooks, Robust AI’s robots are designed to collaborate with humans in factories and warehouses.
We use cookies to run the site and, with your consent, for analytics and to show ads.
See our Cookie Policy.