Skip to content

CyberRoBERTa: A Lightweight Transformer-Based Language Model for IoT Intrusion Detection

Oct 2026 · Italian National Conference on Sensors · Vol 26, pp. 6326 · 0 citations · 34 references
Medicine

TL;DR

CyberRoBERTa is presented, built specifically to test whether departing from off-the-shelf LLM components, through a domain-specific Unigram tokenizer and an IoT-specialized data collator, yields a genuine advantage for IoT intrusion detection.

Abstract

With the accelerated proliferation of the Internet of Things (IoT) and its widespread use in sensitive areas such as healthcare, homes, and factories, security has become an increasingly critical concern. IoT remains one of the most challenging domains to secure, lacking the manageable scale, well-maintained software, and homogeneous environments of easily secured systems. Large language models (LLMs) have recently been applied to improve IoT security; however, most applications treat LLMs as “off-the-shelf” tools, creating a domain mismatch because model representations, tokenizers, and data collators are designed for natural language rather than network traffic. In this work, we present CyberRoBERTa, built specifically to test whether departing from off-the-shelf LLM components, through a domain-specific Unigram tokenizer and an IoT-specialized data collator, yields a genuine advantage for IoT intrusion detection. We instantiate this framework as a compact, 10.2-million-parameter model designed for fully self-contained, on-device operation. Using CICIoT2023, TON_IoT, and Edge-IIoTset, the model achieves a binary classification F1-score of 96% and a multiclass F1-score of 89.54%. We further validate these results in three ways: a comparison against a classical machine learning baseline shows comparable accuracy; isolating the tokenizer’s contribution from pretraining scale shows its benefit holds under matched pretraining conditions; and evaluating class-imbalance interventions shows improved detection on the most data-scarce class.
Read PDF

Similar papers

#machine learning Preprint Sep 2026

An LLM-Assisted AutoML Framework for Intrusion Detection in IoT Networks

Internet of Things (IoT) systems are increasingly deployed in smart homes, transportation, energy systems, and critical infrastructure. This broad connectivity improves service intelligence, but also enlarges the attack surface of IoT networks. Machine Learning (ML)-based Intrusion Detection Systems (IDSs) are widely u...

Li Yang · 0 citations
Conference Open access 2026

Scalable and Efficient Security Solutions for IoT Networks: An Adaptive Machine Learning Approach

The number of Internet of Things (IoT) devices has grown at a rapid pace and has created a larger attack surface for modern networks, making them an appealing target for botnets, ransomware, and distributed denial-of-service (DDoS) attacks. While traditional IDSs are typically built with a centralized machine learning...

J. J. Patil, Prajakta P. Shirke · 0 citations
#artificial intelligence Preprint Sep 2026

CESBench: Benchmarking Large Language Models on Cryptographic Engineering Security for IoT Devices

This paper presents CESBench, 380 expert-written items across six sub-domains of cryptographic engineering security for IoT devices: side-channel, fault injection, implementation, countermeasures, evaluation, and integration, and presents the benchmark, prompts, and per-item results.

Wen-Quan Zhou, An Wang, Jing-Ping Liang et al. · 0 citations
#explainable ai Review Open access Sep 2026

Explainable AI-Based Intrusion Detection Systems for IoT Environments: A Systematic Literature Review

This paper aims to provide a foundational resource to guide future research on reliable, explainable, and practical IoT intrusion detection systems by identifying the problems addressed in current research and highlighting the limitations in the literature.

Murat Varol, Aykut Karakaya · 0 citations
#federated learning Review Open access Sep 2026

Cyber Attacks in the Internet of Things (IoT) and Intelligent Defense Mechanisms

The findings of this review show that proactive, cooperative, and self-healing security mechanisms are more effective than traditional reactive approaches in IoT environments and provide recommendations for developing scalable, energy-efficient, and privacy-preserving IoT security frameworks for future research.

Esraa Ward, Seyed Amin Hosseini Seno · 0 citations

Related blog posts

Microsoft Research Blog Oct 12, 2026

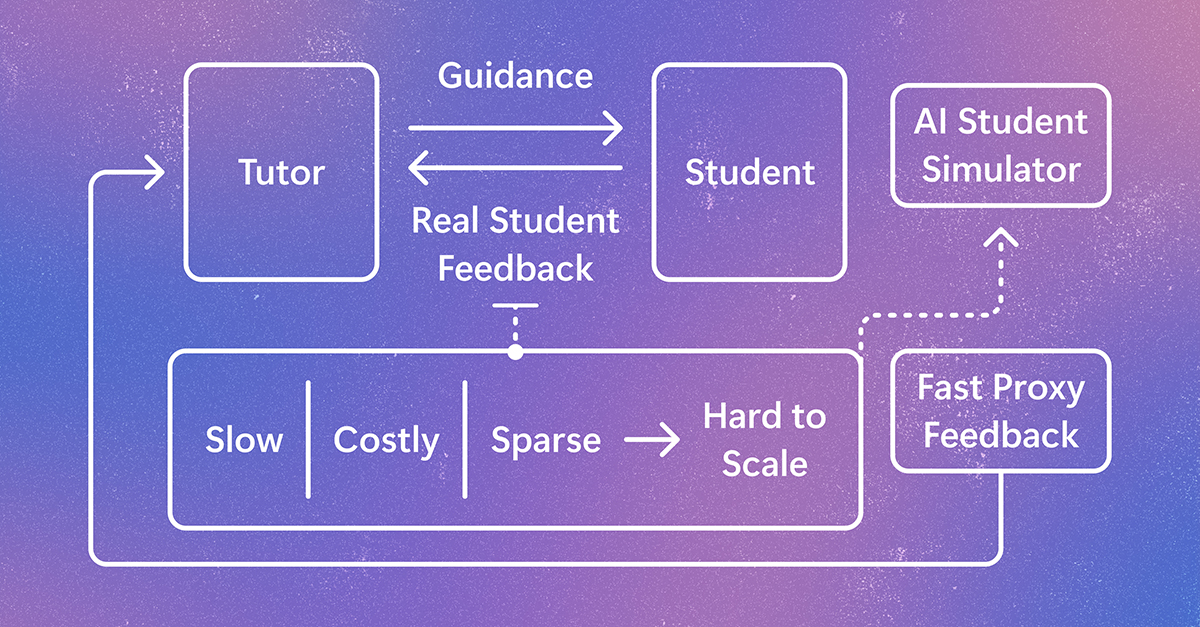
Simulating student learning for better AI tutoring

StudentSim is a research system for evaluating and improving AI tutoring tools before they are tested with learners. It models how individuals may engage with tutors, giving feedback to improve tutor performance across subjects like chess, writing, and mathematics. The post Simulating student learning for better AI tutoring appeared first on Microsoft Research.

GPT-Lab Sep 23, 2026

Requirements Don’t Live in Isolation: What We’re Exploring with Req-Space

Requirements in large systems rarely exist in isolation. Their meaning depends on the wider project context - other requirements, policies, decisions, tests, and implementation details. That becomes especially important when AI is used for review, because spotting a possible conflict or gap is only the beginning. ReqSpace explores how AI, visualisation, and connected project context can help reviewers understand those findings, trace the relationships behind them, and focus on the questions that…

We use cookies to run the site and, with your consent, for analytics and to show ads. See our Cookie Policy.