Skip to content
#software testing Review Open access

Infrastructure as Code Security: A Review of Automation, Compliance, and Risk Management

Sep 2026 · International Research Journal of Medical Sciences and Health Care · 0 citations

TL;DR

The review underscores the importance of implementing secure, scalable, and reliable IaC practices that incorporates automation, compliance, validation, and risk management in the infrastructure lifecycle.

Abstract

Infrastructure as Code (IaC) has become an important approach for automating the provisioning, configuration, validation, and management of cloud and software infrastructure. This review covers five aspects of IaC: DevOps integration, security, automation, compliance, validation, and risk management. By version controlling, testing, validating, and automating the deployment of infrastructure configurations, IaC makes infrastructure changes and deployments more efficient and automated, which enables continuous integration and continuous deployment. Security considerations include misconfigurations, hardcoded secrets, inadequate access controls, vulnerable third-party modules, supply-chain attacks, and configuration drift. Infrastructure governance is reinforced by automation and compliance mechanisms that validate the infrastructure in the interest of a policy, check the compliance at runtime, and enforce the policy automatically. Automated validation embeds shift-left principles, static analysis, unit testing and policy-as-code to catch errors and violations before they reach the end-users. The other elements of risk management are identification of risk, configuration drift, vulnerability management, risk assessment, threat detection and continuous risk monitoring. In conclusion, the review underscores the importance of implementing secure, scalable, and reliable IaC practices that incorporates automation, compliance, validation, and risk management in the infrastructure lifecycle. These practices help reduce human error, ensure deployment uniformity, adhere to regulatory requirements, and enhance organizational resilience through sustainable infrastructure security, auditability, flexibility and suitability for changing operational needs.
Read PDF

Similar papers

Open access Sep 2026

Secure DevOps for Financial Middleware: Integrating Compliance into CI/CD Pipelines

Aim: This study proposed a Secure DevOps model for financial middleware that integrates automated security controls and regulatory compliance mechanisms into Continuous Integration and Continuous Deployment (CI/CD) pipelines. Methods: The study adopted a proposal-based architectural approach to design a security- and...

Rang Ganesh Singh Alampur · 0 citations
#software testing Review Open access Sep 2026

DevSecOps: A Comprehensive Survey of Secure Software Development and Deployment Practices

DevSecOps brings together development, security, and operations approaches to incorporate security across the software development lifecycle, allowing organizations to discover and address vulnerabilities earlier while ensuring quick and dependable software delivery. This survey reviews the foundations, practices, tech...

Prashant Kumar Shrivastava · 0 citations
Conference Aug 2026

Integrating Observability, DevSecOps, and Policy-as-Code for Enterprise Cloud Reliability

Modern enterprise cloud infrastructures need to be able to deliver software quickly, remain operationally resilient and follow strict regulatory requirements. Through traditional operations, observability, security and governance are typically treated as separate processes, which leads to longer Mean Time To Repair (MT...

Vishwa Lakhnakiya · 0 citations
Review Open access Aug 2026

Securing CI/CD Pipelines: A DevSecOps Framework for Preventing Credential Leaks and Misconfigurations

This study investigates security risks in Dock-er-based GitHub Actions workflows and proposes a tailored, DevSecOps-aligned security checklist to mitigate these threats, offering practical protection against supply-chain threats while preserving delivery speed and scalability.

A. Amirova · 0 citations
Open access Sep 2026

An Author’s Taxonomy of Customer-Observable Security Controls in SaaS Platforms

A taxonomy that classifies security controls for SaaS platforms by the degree to which they are observable to the tenant is introduced, giving tenants a shared language for procurement, contractual negotiations, and continuous assurance, and gives providers a roadmap for increasing visibility into their controls.

Sergei Beliachkov · 0 citations
Preprint Sep 2026

Measuring the Security of the Evolving Software Supply Chain: a Research Agenda

Software supply chain security has become increasingly critical due to the widespread reliance on third-party dependencies and the growing attack surface of modern software ecosystems. However, existing quantitative, measurement-based analysis and vulnerability management approaches remain largely fragmented and ecosys...

Sarah Meriem Ourari · 0 citations

Related blog posts

Microsoft Research Blog Oct 12, 2026

Simulating student learning for better AI tutoring

StudentSim is a research system for evaluating and improving AI tutoring tools before they are tested with learners. It models how individuals may engage with tutors, giving feedback to improve tutor performance across subjects like chess, writing, and mathematics. The post Simulating student learning for better AI tutoring appeared first on Microsoft Research.

MIT News · Artificial Intelligence Oct 2, 2026

Documenting the tech worker movement

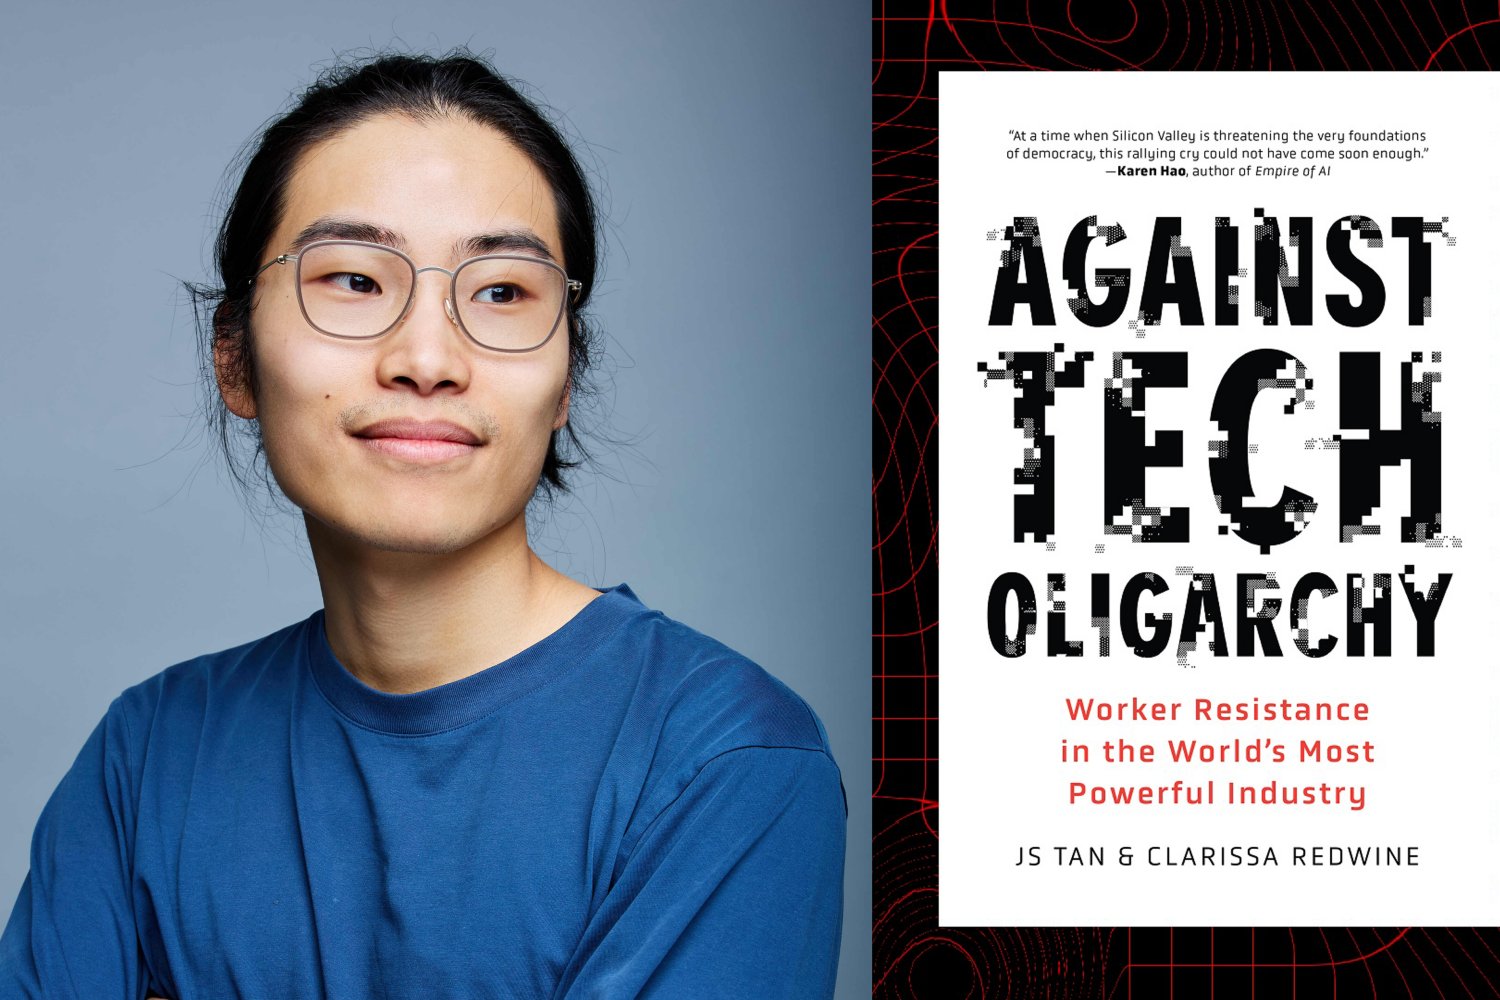
Writing as a participant and researcher, PhD student JS Tan SM ’22 has co-authored a new book about the rise of tech worker protests and the employer backlash that followed.

MIT News · Artificial Intelligence Oct 2, 2026

Documenting the tech worker movement

Writing as a participant and researcher, PhD student JS Tan SM ’22 has co-authored a new book about the rise of tech worker protests and the employer backlash that followed.

We use cookies to run the site and, with your consent, for analytics and to show ads. See our Cookie Policy.